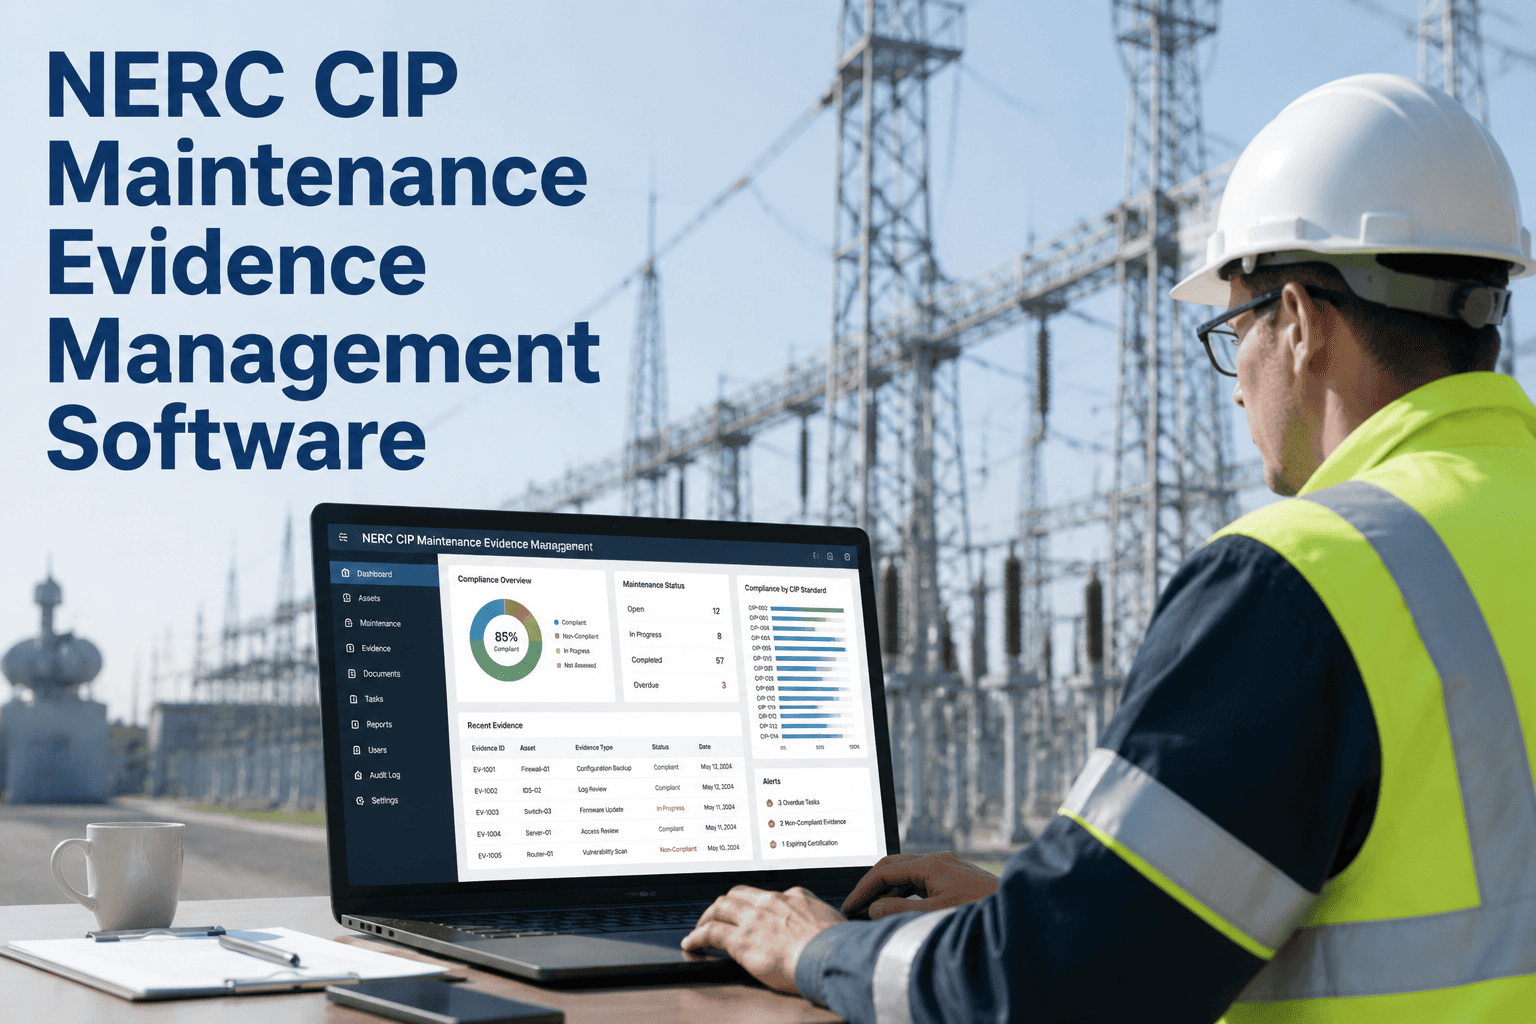
NERC CIP compliance is not tested once and filed away. It is an ongoing operational obligation — CIP-006 physical security logs, CIP-007 system access reviews, CIP-010 baseline configuration comparisons, and corrective action records must be available, organized, and attributable at every quarterly and annual review. The utilities that receive audit findings overwhelmingly share one characteristic: their evidence exists but is not packaged. It lives in email threads, shared drives, and printed binders that take days to assemble on demand. If that describes your program today, the risk is already real. Start your OxMaint free trial and build a NERC CIP evidence pack your team can produce in minutes, not days.
NERC CIP · CIP-006 · CIP-007 · CIP-010 · Compliance Evidence
Free NERC CIP Compliance Evidence Pack Template — Audit-Ready Records for CIP-006, CIP-007, and CIP-010
A structured evidence pack template covering physical security logs, system access records, baseline configuration comparisons, and corrective action trails. Download the template — then see how OxMaint routes every evidence item directly from operational activity to audit-ready documentation.
CIP Evidence Pack — Audit Status
CIP-006
Physical Access Logs
Complete
CIP-006
Visitor Authorization Records
Complete
CIP-007
System Access Review
Gap Found
CIP-007
Patch Management Evidence
Complete
CIP-010
Baseline Configuration Log
Missing
CIP-010
Change Authorization Records
Complete
What Is at Stake
NERC CIP Violations Are Expensive — And Most Are Documentation Failures, Not Security Failures
$1M+
Per-day penalty ceiling for serious CIP violations
NERC has authority to impose civil penalties up to $1 million per violation per day. Documentation gaps that span multiple compliance periods compound quickly.
~60%
Of CIP findings relate to incomplete or missing evidence
The activity was performed. The record was not produced or was not retrievable in the format auditors require. That distinction does not reduce the finding.
3–5 Days
Average time to assemble evidence manually for a mid-size utility
For utilities with 50 or more BCSI assets across multiple substations, manual evidence assembly is not just slow — it is structurally unreliable under audit pressure.
CIP-007
Most frequently cited standard in NERC enforcement actions
System security management — including access control, ports and services, and patch management — produces the highest volume of evidence documentation requirements per compliance period.
The Evidence Pack Template
What the NERC CIP Compliance Evidence Pack Template Contains — Standard by Standard
The template is organized by CIP standard and requirement. Each tab covers the evidence items, record fields, and documentation notes your compliance team needs to satisfy the relevant requirement during an audit or self-certification review.
CIP-006
CIP-007
CIP-010
Asset List
Corrective Actions
R1
Physical Security Plan documentation with applicable Electronic Security Perimeters and Physical Security Perimeters identified
R2
Visitor log entries: name, escorted-by, entry time, exit time, purpose — retained for minimum 3 calendar years
R3
Physical access log exports covering all access points into the Physical Security Perimeter for the compliance period
R4
Access authorization review records — quarterly reviews of personnel with physical access rights, with approval signatures
R5
Alarm or alerting system maintenance records and test logs for monitoring systems protecting the Physical Security Perimeter
R1
Ports and services documentation: list of enabled ports per device, justification for each, review date and approver
R2
Security patch assessment records: patch source review date, applicability determination, remediation plan or acceptance decision
R3
Malicious code prevention evidence: solution identification, update status log, and exception documentation where applicable
R4
Security event monitoring configuration and log retention evidence — 90-day minimum retention with review records
R5
System access control records: account inventory, shared account justifications, quarterly access review with approver sign-off
R1
Baseline configuration documentation per BES Cyber Asset: OS version, installed software, logical ports, security patches applied
R1
Change authorization records: change description, pre-change baseline snapshot, post-change verification, approver, and date
R2
Active baseline comparison evidence — records of periodic comparisons to detect unauthorized changes between formal change events
R3
Vulnerability assessment records: assessment date, method, scope, findings, and remediation or acceptance rationale — annual for High and Medium impact
R4
Transient cyber asset authorization and protection documentation for devices connected to applicable BES Cyber Systems
ID
Unique asset identifier, asset name, asset type (BCA, EACMS, PACS, PCA), and physical location
Class
Impact classification — High, Medium, or Low — with classification rationale and date last reviewed
ESP
Electronic Security Perimeter assignment and Physical Security Perimeter assignment per asset
Owner
Responsible engineer or team, most recent change date, and applicable CIP standards by row
R1
Gap description: which requirement, what was missing or incorrect, date identified and identified-by
R2
Corrective action assigned: responsible party, planned resolution date, mitigation steps documented
R3
Resolution evidence: completion date, verification method, approver sign-off, and closure timestamp
R4
Root cause analysis for High and Medium impact findings — process change documented to prevent recurrence
OxMaint · NERC CIP · CIP-006 · CIP-007 · CIP-010 · Evidence Automation
Your CIP Evidence Should Be One Click Away. OxMaint Makes It So.
OxMaint routes every maintenance activity, access review, patch record, and corrective action directly into a structured evidence pack — exportable on demand, no assembly required. See it in 30 minutes.
Where Evidence Gaps Actually Come From
The Four Evidence Patterns That Produce CIP Audit Findings — And How OxMaint Closes Them
CIP-006
Physical Access Logs With Incomplete Entries
Visitor logs missing exit times, escorted-by fields not completed, or access reviews without a dated approver signature — all produce R2 and R4 findings regardless of actual physical security quality.
OxMaint enforces required fields at the point of entry. A work order cannot close without complete attribution. Every access event is timestamped and linked to the responsible record automatically.
CIP-007
Quarterly Access Reviews Not Documented
CIP-007 R5 requires quarterly reviews of accounts with access to applicable BES Cyber Systems. When reviews happen verbally or via email without a formal record capturing reviewer identity and outcome, the review never happened from an audit perspective.
OxMaint generates quarterly access review work orders automatically. Completion requires capturing the reviewer, the review outcome, and any accounts removed — producing the structured record CIP-007 requires without additional process steps.
CIP-010
Baseline Changes Without Authorization Records
CIP-010 R1 requires documenting the authorization and verification of every change to a BES Cyber Asset baseline. Emergency changes made outside the change management process — and changes made by contractors without record handover — are the most common source of CIP-010 findings.
OxMaint captures change authorization at work order creation. Contractor-performed work is documented under the issuing engineer's record. Emergency work orders still require authorization fields before closure — eliminating unrecorded baseline changes.
CAP
Corrective Actions Without Formal Closure Evidence
Self-identified compliance gaps that were verbally addressed, fixed without a written corrective action plan, or closed without documented verification create a second finding on top of the original gap. Auditors treat an undocumented corrective action the same as no corrective action.
OxMaint routes every compliance gap finding to a formal corrective action work order with a responsible party, planned date, and required closure evidence. The full CAP trail — from identification to verified closure — is retained and exportable.
Pre-Audit Readiness Check
NERC CIP Evidence Pack Readiness — 12 Items to Verify Before Every Audit
CIP-006 Physical Security
Physical Security Plan is current and reflects all active PSPs and ESPs
Visitor logs complete with all required fields for past 3 years
Quarterly physical access reviews documented with approver and date
Alarm and monitoring system maintenance records retained
CIP-007 System Security
Ports and services documentation current for all applicable assets
Security patch assessments completed within 35-day window and documented
CIP-007 (continued)
Quarterly account access reviews documented — all required fields completed
Security event log retention meets 90-day minimum with review records
CIP-010 Configuration Management
Baseline configurations documented per BES Cyber Asset — current versions verified
All changes from the compliance period have authorization records and post-change verification
Annual vulnerability assessment records complete with findings and disposition
All open corrective actions have formal CAP records with responsible party and target date
OxMaint · NERC CIP Evidence · Free to Start · No IT Overhead
Stop Assembling Your CIP Evidence Pack Under Audit Pressure.
OxMaint structures every maintenance activity, access review, patch record, and corrective action into a NERC CIP evidence pack that is exportable, timestamped, and auditor-ready on demand. Go live across your full BES Cyber Asset register — no lengthy implementation, no IT project required.
Frequently Asked Questions
NERC CIP Evidence Pack — Common Questions
Does the evidence pack template cover all three standards — CIP-006, CIP-007, and CIP-010?
Yes. The template includes separate sections for each standard organized by requirement number. CIP-006 covers physical access logs and visitor records. CIP-007 covers ports and services, patch management, and quarterly access reviews. CIP-010 covers baseline configurations, change authorization, and vulnerability assessments. A shared corrective action register and asset list tab complete the pack.
Start a free trial to see how OxMaint structures this automatically.
How does OxMaint route maintenance activities into a CIP evidence pack without manual steps?
Every work order in OxMaint is attributed to an asset, a responsible technician, and a completion timestamp at closure. When the asset is tagged to an applicable CIP standard, that work order automatically contributes to the evidence record for that requirement. The evidence pack export filters by standard and date range — no document gathering required.
See the evidence routing workflow in a live demo.
What is the most common source of CIP-007 findings and how does OxMaint address it?
CIP-007 R5 quarterly account access reviews are the most frequently cited finding category. The most common failure mode is a review that occurred informally — verbally or via email — without a structured record capturing the reviewer identity, review date, and account disposition. OxMaint generates the quarterly review work order automatically and enforces completion of all required fields before the record closes.
Can OxMaint generate a CIP-010 baseline change history for a specific asset during an audit?
Yes. Filtering by asset and date range in OxMaint produces the complete change authorization history for that BES Cyber Asset — including the pre-change baseline state, post-change verification, authorization approver, and timestamp for every documented change in the period.
Start free and run a sample export against your asset register.