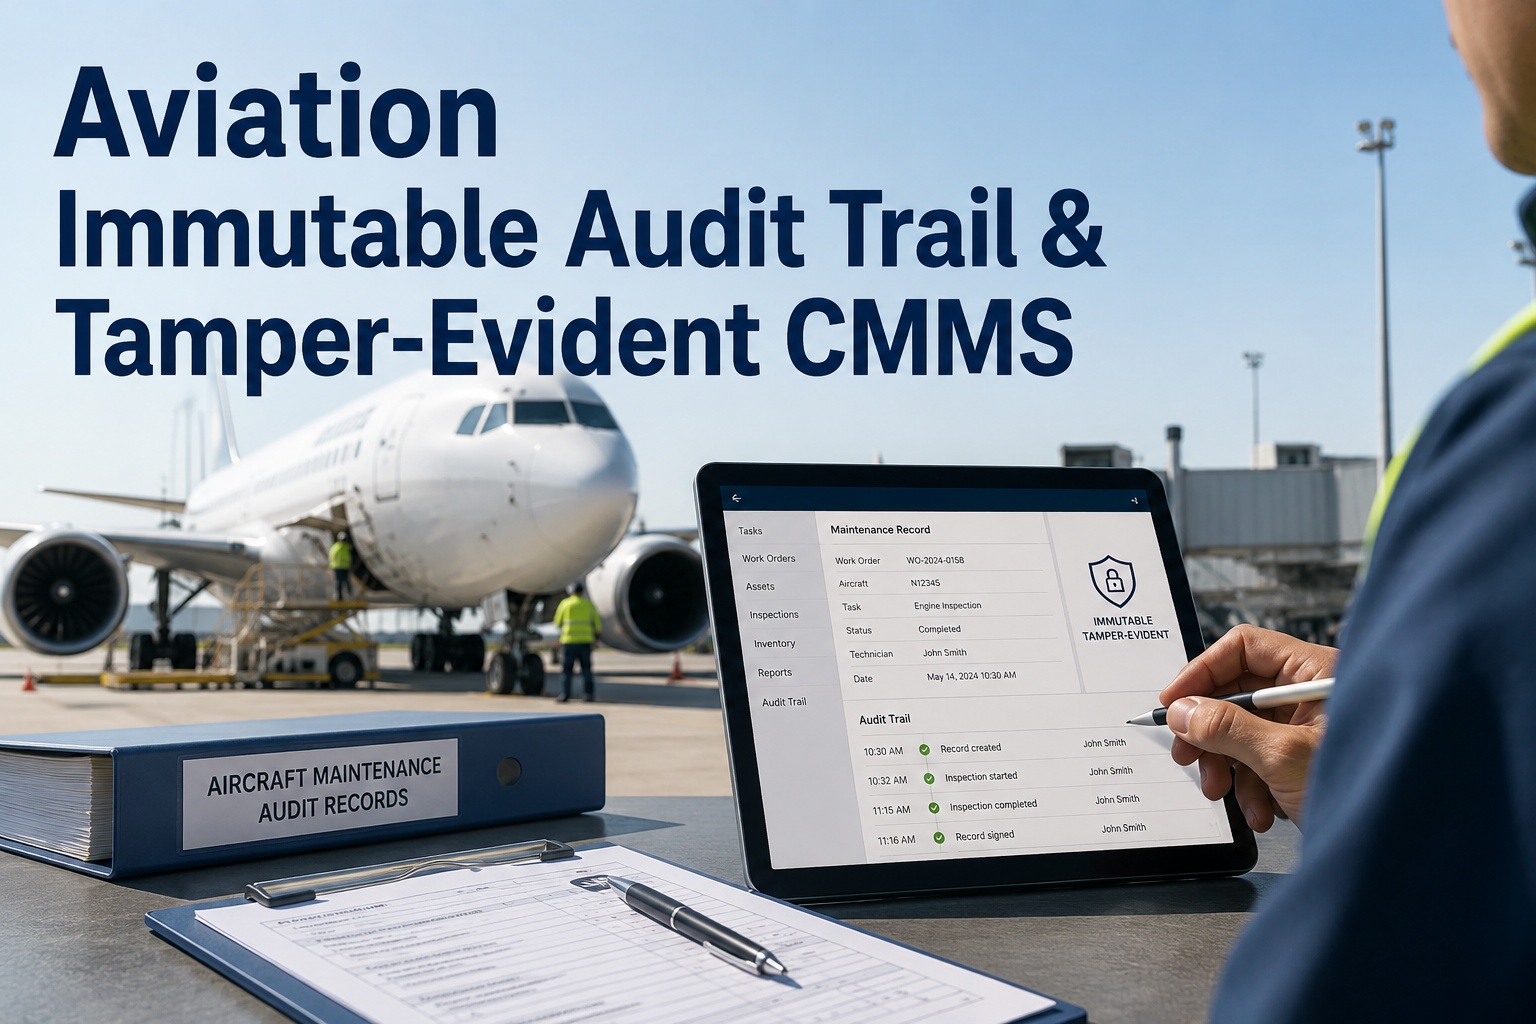
An aviation immutable audit trail is the cryptographic backbone that separates a defensible, tamper-evident CMMS from a digital paper system with better fonts. For airlines and MROs, maintaining immutable records ensures that every maintenance action, sign-off, and parts change is permanently recorded, encrypted, and compliant with stringent FAA and EASA record-integrity expectations. This CMMS immutable guide for 2026 breaks down how audit trail encryption, WORM (Write Once, Read Many) storage, and SOC 2 compliance protect your operations from data tampering and costly compliance failures. Discover how modern audit-traceable CMMS platforms eliminate IT trust dependencies, or start securing your maintenance data today when you Start Free Trial.
CMMS Immutable Guide 2026
Can your maintenance records survive a forensic audit without blind trust in IT?
A tamper-evident CMMS uses cryptographic sealing and encrypted data at rest to ensure every work order entry, e-signature, and asset change is permanently locked. If a record can be silently edited, it is not an audit trail—it is a liability.
Record Integrity via Cryptographic Sealing
The Cost of Mutable Records
Why aviation maintenance requires a tamper-evident CMMS
In aviation maintenance, a single altered timestamp or backdated sign-off can trigger FAA or EASA enforcement actions, costing an MRO upwards of $250,000 per violation and grounding entire fleets. Traditional CMMS platforms rely on standard database logs that database administrators can edit, delete, or overwrite—making them fundamentally unreliable for defensible audit traceable documentation. An aviation immutable audit trail solves this by applying cryptographic hashes to every transaction. Once a technician logs a preventive maintenance task or closes a work order, the system locks the data using WORM storage and e-signature evidence. This tamper-evident architecture ensures that any unauthorized modification is immediately visible to auditors, shifting the trust from IT personnel to verifiable mathematics.
Average cost per FAA record-keeping citation
Time lost proving compliance with paper or mutable logs
Edits allowed without cryptographic breakage
Architecture & Standards
How an immutable audit trail works in aviation CMMS
Building an immutable trail in 2026 requires moving beyond basic change-history preservation. A true audit-traceable CMMS layers multiple security protocols to guarantee data integrity from the moment a mechanic interacts with the system to the decade-long retention period required by regulators.
Cryptographic Hash Sealing
Every work order update generates a SHA-256 hash tied to the previous entry. If a single character in a spare parts inventory record changes, the hash chain breaks, instantly alerting auditors to tampering.
WORM Storage Architecture
Write Once, Read Many storage guarantees that completed maintenance logs and e-signatures cannot be overwritten. Data is committed permanently, satisfying strict FAA retention rules without IT intervention.
E-Signature Evidence Chains
Dual-factor e-signatures are bound to the exact state of the asset record at the time of signing. The CMMS SOC 2 controls ensure sign-offs cannot be dissociated from their underlying maintenance data.
End-to-End Audit Trail Encryption
AES-256 encryption at rest and TLS 1.3 in transit ensure that immutable records aviation teams rely on are invisible to unauthorized users, protecting sensitive operational data from external breaches.
Scenario Analysis
Immutable records vs traditional CMMS audit logs
A regional MRO operating 180 aircraft was spending $42K annually on manual audit preparation and compliance remediation due to gaps in their standard CMMS change-history logs. By migrating to a tamper-evident CMMS architecture, they eliminated IT trust dependencies and passed a surprise EASA base audit in under 48 hours. Below is how a true immutable trail 2026 standard compares to legacy systems.
| Capability | Standard CMMS Logs | Tamper-Evident CMMS |
|---|---|---|
| Data Modification | Admins can edit or delete history | Cryptographically sealed and permanent |
| Audit Preparation | Weeks of manual data extraction | Instant generation of defensible reports |
| E-Signature Integrity | Detached from record state | Cryptographically bound to asset state |
| Storage Architecture | Mutable relational database | WORM-compliant immutable storage |
| Regulatory Trust Model | Relies on IT personnel honesty | Relies on verifiable mathematics |
Implementation Timeline
How to deploy a CMMS immutable guide for 2026 compliance
Transitioning from a mutable spreadsheet or legacy database to an immutable trail architecture does not require a multi-year IT overhaul. Airlines and MROs can achieve full audit-traceable CMMS compliance in a structured 90-day rollout.
Asset & Data Mapping
Import all aircraft tail numbers, spare parts inventory, and preventive maintenance schedules into the OxMaint EAM platform. Baseline data is hashed to establish the starting cryptographic state.
E-Signature & Workflow Lock
Deploy mobile work order closures with enforced dual-factor e-signatures. Configure WORM storage policies so that any completed task immediately becomes a permanent, immutable record.
Audit Readiness & SOC 2
Activate automated compliance reporting. Run a mock FAA/EASA inspection using the audit trail encryption logs to verify zero gaps and 100% change-history preservation.
OxMaint Solution
How OxMaint secures your aviation maintenance data
OxMaint is an AI-powered CMMS and Enterprise Asset Management platform engineered specifically for high-stakes maintenance and reliability teams. By integrating tamper-evident 2026 standards directly into daily workflows, OxMaint transforms compliance from a costly burden into an automated byproduct of good maintenance practices.
Cryptographic Work Order Sealing
Outcome: Every work order update and technician note is hashed and sealed. Eliminates backdating disputes and cuts audit preparation time by 90%.
Predictive Maintenance Audit Links
Outcome: AI-driven failure predictions are permanently linked to the asset's historical service record. Proves to regulators that predictive interventions were data-backed.
Immutable Spare Parts Tracking
Outcome: Serialized rotable parts maintain a permanent lifecycle ledger. Prevents the use of untraceable components and avoids $50K+ FAA parts violations.
SOC 2 Type II Compliance Engine
Outcome: Continuous monitoring and encrypted data at rest/ in transit. Passes external security audits without manual log scraping or IT intervention.
Stop trusting your maintenance records to editable databases.
See how OxMaint builds an unbreakable, audit-ready trail across every asset, work order, and parts transaction.
Frequently Asked Questions
Aviation immutable audit trail & CMMS compliance
What makes an aviation CMMS audit trail truly immutable?
A truly immutable audit trail uses cryptographic hash sealing (like SHA-256) and WORM (Write Once, Read Many) storage. This means once a maintenance record, e-signature, or parts change is committed to the CMMS, it cannot be altered or deleted—even by database administrators—without visibly breaking the hash chain. This satisfies FAA and EASA record-integrity expectations without relying on blind trust in IT.
How does a tamper-evident CMMS help during FAA and EASA audits?
A tamper-evident CMMS provides auditors with instant, verifiable proof that maintenance data has not been tampered with. Instead of spending days manually extracting and validating logs, compliance teams can generate a cryptographically secure report in minutes. To see this reporting in action, you can Book a Demo with our aviation compliance team.
What is the difference between SOC 2 compliance and an immutable trail in 2026?
SOC 2 compliance focuses on the overarching security, availability, and confidentiality controls of a software platform (like encryption at rest and in transit). An immutable audit trail is a specific data-integrity feature within that framework ensuring individual records cannot be altered. A CMMS that is SOC 2 compliant with an immutable trail provides both high-level security and record-level defensible documentation.
Can we migrate historical maintenance logs into an immutable CMMS?
Yes. When migrating from legacy systems or paper, historical maintenance logs are imported into the CMMS and immediately hashed to establish a baseline cryptographic state. While the previous history cannot be retroactively proven as immutable, all future changes, sign-offs, and updates to those records will be permanently sealed and audit-traceable.
Does audit trail encryption slow down daily maintenance workflows?
No. Modern audit trail encryption and hashing occur at the database layer in milliseconds. Mechanics and technicians interacting with the CMMS via mobile devices will experience no perceptible latency when closing work orders or signing off on preventive maintenance tasks. You can test the system's speed yourself when you Start Free Trial.
Secure your maintenance data with OxMaint today.
Deploy a tamper-evident CMMS that protects your assets, passes audits, and eliminates IT trust risks.
Free 14-day trial · No credit card