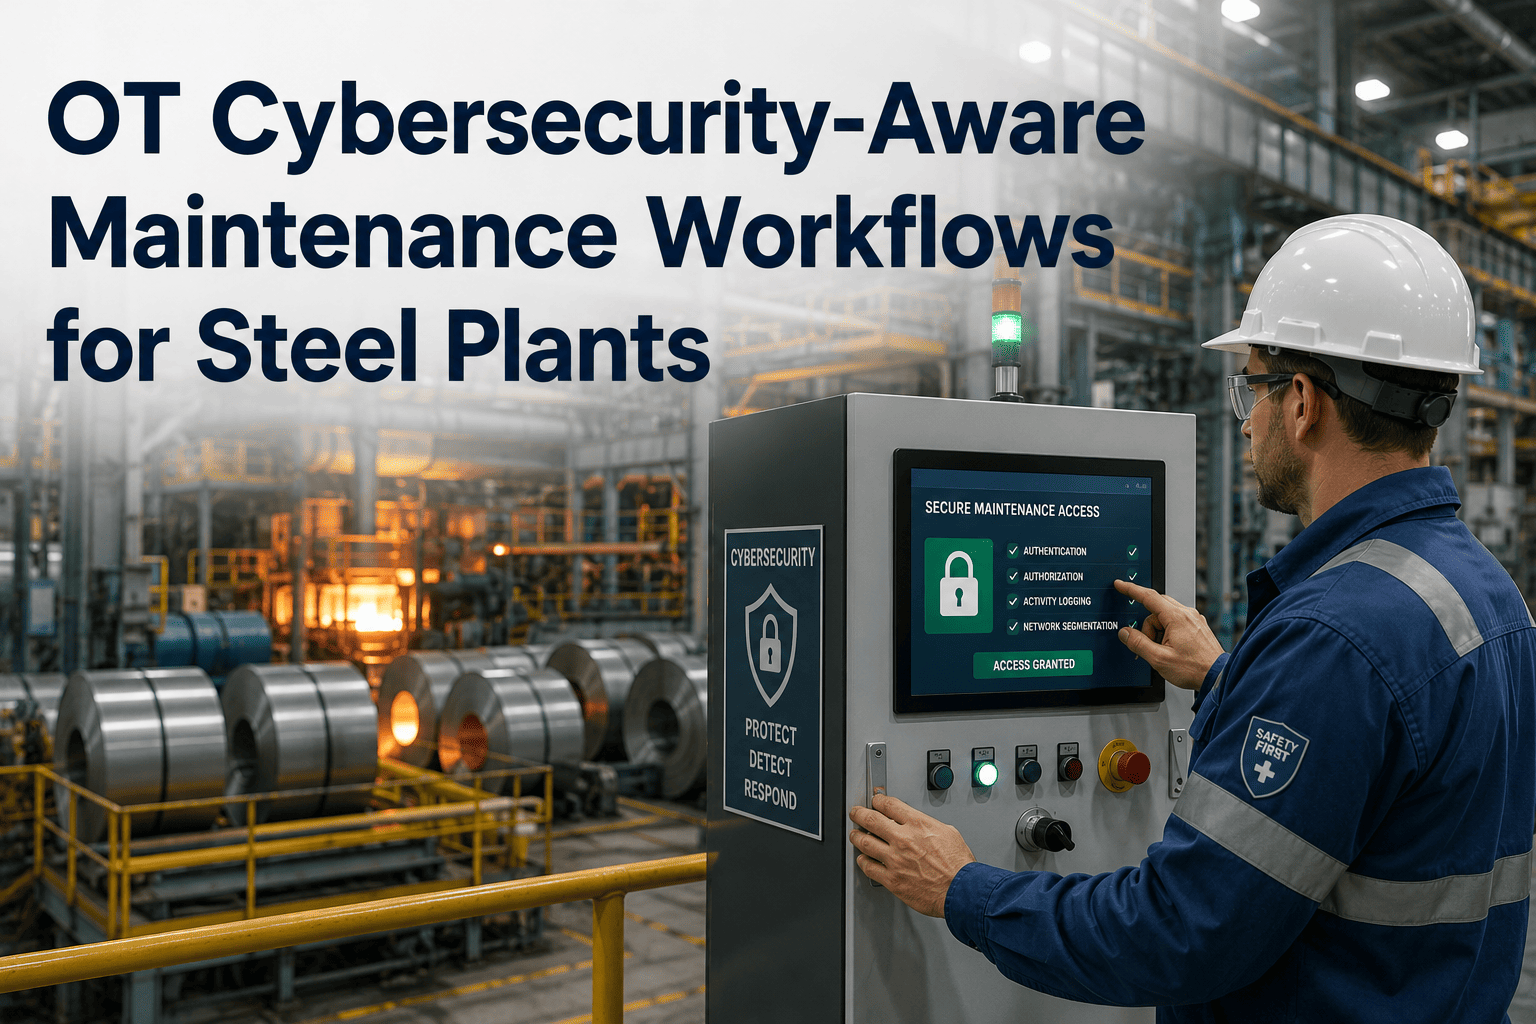
In the high-stakes world of North American steelmaking, the era of the "air-gap"—the physical isolation of industrial control systems from the internet—is officially over. The convergence of Information Technology (IT) and Operational Technology (OT) has enabled unprecedented efficiency gains in OEE and predictive maintenance, but it has also opened the door to sophisticated cyber-physical threats that target critical infrastructure. For a modern integrated mill or high-speed mini-mill, cybersecurity is no longer just an IT checkbox; it is a fundamental pillar of operational reliability, worker safety, and B2B trust. A single ransomware attack on a SCADA network or a compromised PLC in a caster or rolling mill can lead to weeks of unplanned downtime, multi-million dollar recovery costs, and potential life-safety breaches. Implementing a structured cybersecurity program based on the NIST Cybersecurity Framework (CSF) and IEC 62443 is essential for protecting the facility's bottom line. By utilizing an industrial CMMS to track cybersecurity PMs, patch cycles, and OT asset inventories, maintenance leaders can ensure their facility remains "Audit-Ready" and resilient against the evolving landscape of global industrial cyber threats. Beyond simple firewalls, true resilience requires a deep integration of security protocols into the physical maintenance routine. This includes the systematic verification of PLC firmware integrity, the encryption of industrial sensor data, and the rigorous governance of third-party remote access. Start Your Cyber-Audit with OxMaint and gain 100% visibility into your digital and physical asset risks. Sign Up Free
Steel Plant OT Cybersecurity: NIST CSF & IEC 62443 Compliance
Standardize OT Asset Inventory · Automate NIST CSF Patch Management · Document IEC 62443 Audit Trails · Implement Network Segmentation (Purdue Model) · Track SCADA/DCS Backup PMs · Manage Cyber-Physical Risk Assessments · Secure Remote Access Gateways
NIST Cybersecurity Framework: OT Asset Lifecycle
Industrial cybersecurity is a continuous maintenance loop. OxMaint integrates the NIST CSF directly into your maintenance workflow, ensuring that your digital defense evolves as quickly as the threats targeting your mill. Effective lifecycle management starts with identifying "Shadow OT" devices and extends through response playbooks and disaster recovery validation.
Identify: Asset Inventory
Map every PLC, HMI, and industrial switch. Track firmware versions and physical locations to eliminate hidden security gaps. 100% visibility is the first step to a secure OT network.
Protect: Patch Cycles
Automate firmware patching and access reviews. OxMaint ensures that your critical controllers are always updated according to OEM security bulletins and NIST standards.
Detect: IDS Integration
Link Intrusion Detection System alerts directly to your CMMS. Generate high-priority investigation work orders the moment a network anomaly is detected in the OT layer.
Respond: Recovery Playbooks
Pre-defined digital playbooks ensure standardized response. Isolate compromised segments and prevent lateral movement across the mill during a cyber event.
IEC 62443: Defense in Depth (Purdue Model)
Industrial resilience relies on robust network segmentation. By isolating critical process control layers from enterprise IT threats, steel mills can maintain production continuity even during a corporate-wide security breach. OxMaint documents the integrity of these segments through systematic monthly audits of jump hosts, firewalls, and industrial DMZs.
Cybersecurity PM Compliance Matrix
Comprehensive documentation is the heart of regulatory compliance. OxMaint provides a permanent digital audit trail for all cybersecurity-related maintenance tasks, ensuring your facility is always ready for CISA, NERC, or insurance reviews.
| Asset / System | Maintenance / Security Task | Interval | Alignment | Risk if Missed |
|---|---|---|---|---|
| PLC Controllers | Firmware patch verification vs OEM bulletin | Quarterly | NIST CSF | CRITICAL — Exploitable vulnerability |
| SCADA Backups | Backup integrity verification; test recovery | Weekly | IEC 62443 | HIGH — Permanent configuration loss |
| IDMZ Firewalls | Rule audit; remove inactive service accounts | Monthly | Protect | HIGH — Lateral threat movement |
| Asset Inventory | Physical audit of OT devices; update IP logs | Semi-Annual | Identify | MED — Hidden 'Shadow OT' risks |
| HMI Physical Security | Inspect panel locks; disable unused USB ports | Monthly | Physical | HIGH — Local console tampering |
| Access Audit | Review admin privileges for SCADA/DCS | Monthly | Governance | HIGH — Unauthorized config changes |
Document Your Defense. Defend Your Production.
OxMaint converts your cybersecurity policy into a living maintenance program. From automated PLC patching to time-stamped IEC 62443 audit logs, our CMMS ensures your digital defense is as robust as your physical machinery. Build your audit-ready OT inventory in under 30 minutes.
OT Cybersecurity ROI: Avoiding the Outage
In a high-tonnage mill, cybersecurity is a performance lever. By reducing cyber-insurance liability and eliminating the risk of week-long production lockouts, a structured digital security program pays for itself manifold. OxMaint provides the tools to quantify these risks and document the mitigation efforts for executive stakeholders.
"Before OxMaint, our OT assets were invisible to the security team. By building our OT inventory in the CMMS and linking it to our NIST compliance program, we've achieved 100% visibility into every controller in the mill. We've automated our patch cycles and backup verifications, giving us the documented proof we need for our auditors and the peace of mind that our production is protected. It's the only tool we've found that treats cybersecurity with the same operational rigor as mechanical maintenance. The transition to data-driven digital defense was seamless."
Frequently Asked Questions
OxMaint utilizes its 'Asset Management' module to register every PLC, SCADA node, and switch as a trackable parent/child asset.
During setup, teams record IP addresses, firmware versions, and physical location, creating a NIST-compliant inventory updated during every PM work order.
Yes, the system schedules recurring 'Segmentation Audit' work orders for the IDMZ and OT layers to verify that firewall rules are Functioning.
Every audit event creates a permanent digital record that satisfies IEC 62443 requirements for documented evidence of security maintenance and governance.
Unlike IT, OT patching requires careful coordination with production downtime to avoid unplanned asset restarts on critical equipment like caster controllers.
OxMaint manages this by scheduling firmware updates as PM work orders triggered by security bulletins, ensuring execution during planned maintenance windows.
OxMaint manages the backup integrity schedule, ensuring that validated gold-images for all SCADA systems are verified and documented as reachable offline.
In an attack, 'Incident Response' work orders provide digital playbooks to ensure technicians follow standardized, safe restoration procedures to restart production.
OxMaint's logging and reporting framework is specifically designed to satisfy the rigorous evidence requirements of US CISA guidelines and NERC CIP standards.
Our built-in compliance dashboards provide the visibility required for federal audits, proving that your facility's critical infrastructure is defended to national standards.
Physical security is a core pillar of IEC 62443; OxMaint schedules monthly inspections of server room locks, cabinet tamper seals, and port-blockers.
Any physical security violation discovered during these rounds is logged as a high-priority 'Cyber-Physical' work order for immediate investigation and remediation.
Industrial cyber-insurers require documented proof of a mature security maintenance program, including high patch compliance and regular disaster recovery testing.
OxMaint provides the automated performance reporting and historical audit trails that insurers need to verify your 'Low-Risk' status and offer premium reductions.
Through the 'OT Asset Inventory Audit' PM, technicians are required to physically verify every connected device in their assigned zone.
Any device found that does not match the digital twin in OxMaint is flagged as a high-risk 'Shadow OT' asset, triggering an immediate security evaluation.
Don't Wait for the Breach. Defend Your Production.
Join the North American steel leaders using OxMaint to unify their physical maintenance and digital security programs. Your journey to a 100% resilient, NIST-compliant facility starts here. Start your free trial today.