Why the Human-in-the-Loop Mandate Is Driving On-Premise AI Adoption
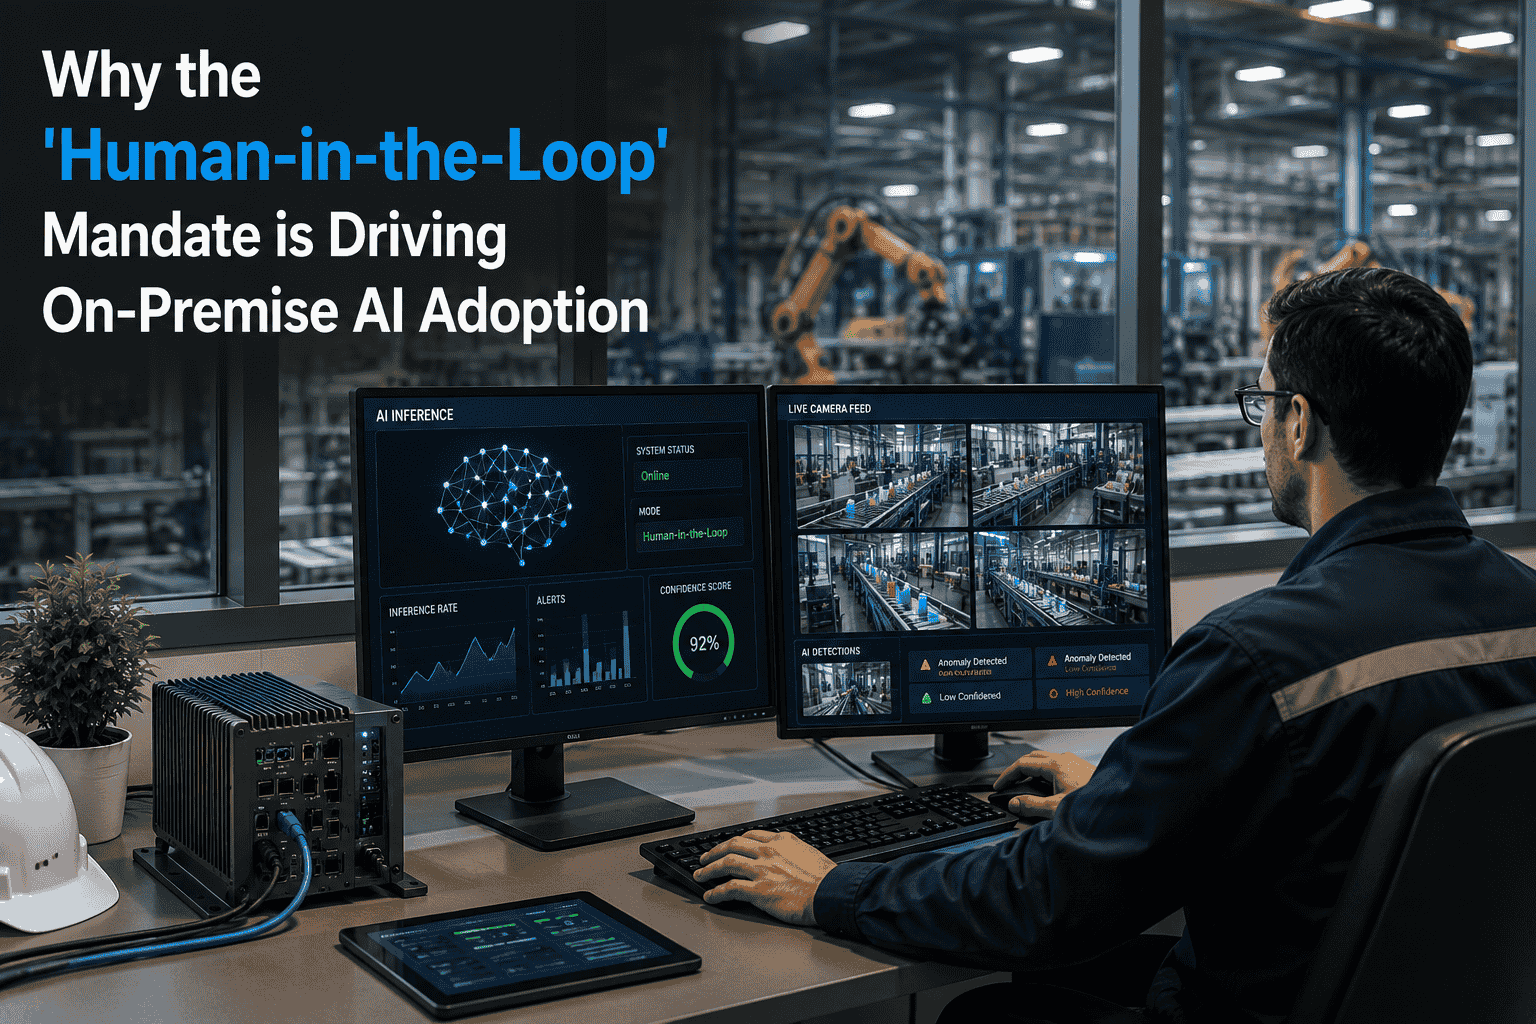
The EU AI Act's August 2026 deadline requires that high-risk AI systems be "effectively overseen by natural persons during the period in which the system is in use." That is Article 14, and it is not a suggestion. The NIST AI Risk Management Framework recommends empowering humans to override AI and monitor outputs regularly. GDPR Article 22 gives individuals the right to request human intervention in automated decisions. More than 700 AI-related bills were introduced in the United States in 2024, with 40+ new proposals in early 2026 — nearly all centering on transparency, override capability, and human oversight. The common thread across every regulation, every framework, and every standard is the same: a human must be able to see what the AI decided, understand why, override it in real time, and prove all of this happened in an audit trail. Cloud-hosted AI makes each of these steps harder. On-premise AI makes each of them natural. That is why the human-in-the-loop mandate is the single largest driver of on-premise AI adoption in 2026. Sign up free to assess your AI governance readiness.
EU AI ACT · NIST RMF · GDPR ART 22 · ISO/IEC 42001
The Regulation Says "Human-in-the-Loop." The Architecture That Delivers It Is On-Premise.
Every major AI governance framework — EU AI Act, NIST RMF, GDPR, ISO 42001 — requires the same five capabilities: input transparency, reasoning visibility, real-time override, audit trail, and feedback loop. Cloud-hosted AI introduces latency, opacity, and jurisdictional complexity at every layer. On-premise AI places the human operator, the AI reasoning, and the audit trail on the same local network, in the same control room, under the same governance perimeter. The mandate is not "use AI responsibly." The mandate is "prove it — in real time, with evidence, under your control."
Anatomy of a HITL-Compliant AI Decision · Five Governance Layers
Every AI decision that touches a high-risk domain — worker safety, product quality, environmental compliance, financial reporting — must pass through five governance layers to satisfy the converging regulations. Each layer has a specific requirement, a specific failure mode under cloud architecture, and a specific reason why on-premise AI is the compliant path. Sign up free to map these five layers to your AI deployment.
1
INPUT TRANSPARENCY
The human can see exactly what data the AI received
THE REQUIREMENT The operator reviewing an AI recommendation must be able to inspect the raw input — the vibration spectrum, the thermal image, the sensor reading, the quality photo — that triggered the recommendation. Without input access, the human cannot evaluate whether the AI's conclusion is reasonable.
CLOUD GAP Input data uploaded to a hyperscaler region. The operator sees a summary or a score — not the raw input. To inspect the underlying data requires cloud portal access, authentication, and often a different interface from the operational dashboard. Latency between input capture and human visibility: minutes.
ON-PREM PATH Input data stays on the plant LAN. The operator's dashboard shows the raw vibration FFT, the thermal image, or the quality photo alongside the AI's recommendation — in the same interface, at the same moment. No cloud portal. No second system. Latency: milliseconds.
2
REASONING VISIBILITY
The human can see why the AI made this recommendation
THE REQUIREMENT EU AI Act Article 13 mandates transparency. The AI cannot be a black box. The human must see which features drove the prediction — which bearing frequency was anomalous, which pixel region triggered the defect classification, which sensor crossed the threshold — and the confidence score.
CLOUD GAP Cloud AI platforms often return a score and a label — "bearing failure · 87% confidence" — without the feature attribution that explains why. Explainability layers (SHAP, LIME, GradCAM) add compute cost and latency in the cloud. Many vendors offer explainability as a premium tier.
ON-PREM PATH The RTX AI Brain runs explainability alongside inference at zero additional latency. The operator sees the prediction, the confidence score, and the feature attribution map — all in the same dashboard frame. "Bearing inner-race frequency at 142 Hz is 7× baseline" — not just "bearing failure."
3
REAL-TIME OVERRIDE
The human can change the AI's decision before it executes
THE REQUIREMENT Article 14 of the EU AI Act requires that the human can "intervene in the operation of the high-risk AI system or interrupt the system." This is not a post-hoc review. It is a real-time override capability — the human must be able to change the AI's decision before the action is taken.
CLOUD GAP Cloud round-trip latency: 100-500ms minimum. For a quality inspection reject at 1,200 bottles/minute, the bottle is past the reject point before the cloud returns the verdict — let alone before a human can review and override. Real-time override through the cloud is architecturally impossible at production speed.
ON-PREM PATH AI recommendation displayed on the operator's HMI within milliseconds. Override button on the same screen. The operator can accept, reject, or modify the AI's recommendation before the action executes. The system waits for human confirmation on high-stakes decisions (configurable per risk level).
4
IMMUTABLE AUDIT TRAIL
Every decision, override, and outcome is recorded with evidence
THE REQUIREMENT The governance framework requires automated capture of: what the AI recommended, what data it used, what the human saw, what the human decided, and what outcome occurred. This audit trail must be tamper-evident, timestamped, and available to regulators upon request.
CLOUD GAP Audit trail stored on multi-tenant hyperscaler infrastructure. Jurisdiction may not match the regulatory authority requesting it. Vendor retention policies may conflict with your compliance requirements. Data export for regulatory review requires vendor cooperation and may incur egress costs.
ON-PREM PATH Audit trail stored on your hardware, in your data center, under your retention policy. Every AI recommendation + human decision + outcome stored with cryptographic timestamps. Available to regulators without vendor intermediation. No egress. No jurisdictional mismatch. You own the evidence.
5
FEEDBACK LOOP
Human corrections improve the model over time
THE REQUIREMENT ISO/IEC 42001 and NIST RMF both require continuous improvement mechanisms. When a human overrides an AI decision, that override becomes training data — the model should learn from the correction and become more accurate over time. This closes the loop between governance and performance.
CLOUD GAP Override data must be uploaded to the cloud for model retraining. Your production-specific corrections train a model that may serve other tenants on a shared platform. Your operational intelligence leaks into a shared training set. Model update timing controlled by the vendor, not by you.
ON-PREM PATH Override data stays on-prem and trains only your model. The DGX Station retrains on your corrections locally. Model versions are controlled by your team. Your operational intelligence never leaves the perimeter. The model gets smarter from your experts — and only your experts.
Art 14
EU AI Act · human oversight during use
Art 13
EU AI Act · transparency of AI systems
NIST
AI RMF · override + continuous monitoring
42001
ISO/IEC · AI management system standard
The five layers are not optional — they are the minimum governance architecture required by the converging regulatory frameworks. A cloud-hosted AI system can satisfy some of them with significant engineering effort. An on-premise AI system satisfies all five by default — because the human, the AI, the data, and the audit trail are in the same room. Book a free demo to see the five governance layers running in the on-prem architecture.
"Our cloud-hosted quality AI rejected a batch of pharmaceutical intermediates worth $2.8M. The quality director wanted to override the rejection and release the batch. The cloud platform had no override mechanism — only an escalation ticket that took 4 hours to resolve."
THE PROBLEM
Pharmaceutical manufacturer. Cloud-hosted AI vision system for intermediate product inspection. The AI flagged a batch of 12,000 units as containing a color deviation outside specification. The quality director — a 22-year veteran with deep domain expertise — examined the physical samples and determined the deviation was within the acceptable range for this specific product-customer combination (a known tolerance documented in the quality agreement). She wanted to override the AI's rejection and release the batch. The cloud platform offered no real-time override. Only an escalation ticket to the vendor's support team. Resolution: 4 hours. During those 4 hours, the batch sat in quarantine, downstream manufacturing halted, and the delivery window for a time-sensitive API shipment closed.
HOW ON-PREM HITL SOLVES IT
Layers 1-2 · Transparency
Quality director sees the raw inspection images, the AI's color-deviation measurement, and the specific pixels that triggered the rejection — all on the local QC dashboard. She can compare the AI's threshold to the customer-specific quality agreement tolerance stored in the plant QMS.
Layer 3 · Override
One-click override on the dashboard: "Release batch — within customer QA tolerance — QD approval." Override takes effect immediately. No escalation ticket. No 4-hour wait. No vendor intermediation. Batch released within 3 minutes of the AI's initial flag.
Layers 4-5 · Audit + Learning
Override logged with: timestamp, operator ID (QD-badge-4471), reason code, customer QA reference, raw image evidence. The override feeds into the next model training cycle — the AI learns this customer's tolerance range and stops flagging it. FDA 21 CFR Part 11-compliant electronic signature captured.
THE RESULT
Override in 3 minutes instead of 4 hours. Batch released. Delivery window met. $2.8M batch saved. Full audit trail. AI learned the customer-specific tolerance.
SCENARIO 02
"Our predictive maintenance AI recommended shutting down a compressor for bearing replacement. The operations manager knew the compressor was running a critical batch that could not be interrupted. He needed to defer the maintenance — not cancel it — and document why."
THE PROBLEM
Chemical plant. Cloud-hosted PdM platform detected bearing degradation on a critical compressor and auto-generated a "shut down for maintenance within 48 hours" recommendation. The operations manager knew the compressor was in the middle of a 72-hour continuous-reaction batch — stopping it would destroy $420K of in-progress product and add 5 days of reactor cleanup. He needed to defer the maintenance to the batch completion window (36 hours out) — not cancel it, and not ignore it. The cloud platform offered no mechanism to acknowledge, defer with a reason, and reschedule. It just kept sending the same "shut down within 48 hours" alert every 4 hours.
HOW ON-PREM HITL SOLVES IT
Layers 1-2 · Transparency
Operations manager sees the FFT spectrum showing the bearing degradation, the RUL estimate (8 days remaining), and the confidence score (91%). He can verify that 36 hours of deferral is within the safe operating window — the RUL gives him 8 days, he only needs 36 hours.
Layer 3 · Defer with Reason
Override: "Defer maintenance 36 hours — batch CRX-4471 in progress — RUL margin sufficient." The AI acknowledges the deferral, increases monitoring frequency on the bearing from 1× per hour to 4× per hour, and reschedules the work order to the batch completion window. Alert stops repeating.
Layers 4-5 · Audit + Outcome
Deferral logged: original recommendation, deferral reason, new target date, increased monitoring decision. After batch completion: bearing replaced successfully during the planned window. Outcome logged: "deferred maintenance completed within RUL window — zero unplanned downtime." Complete governance chain.
THE RESULT
Maintenance deferred 36 hours with documented justification. Batch completed. Bearing replaced on schedule. $420K batch saved. Full governance chain. AI learned the deferral-with-monitoring pattern.
No — the HITL requirement is risk-proportional. Low-risk decisions (routine sensor readings within normal range, standard quality passes) execute automatically with human review available but not required. Medium-risk decisions (maintenance recommendations, production parameter adjustments) flag for human review with a configurable time window. High-risk decisions (batch rejection, equipment shutdown, safety alerts) require human confirmation before execution. The risk classification is configurable per asset, per decision type, and per regulatory requirement.
How does on-prem HITL differ from cloud HITL?
Three architectural differences. First, latency: on-prem presents the AI recommendation + reasoning + override button to the operator in milliseconds; cloud adds 100-500ms minimum round-trip, making real-time override at production speed impossible. Second, audit jurisdiction: on-prem audit trail sits on your hardware under your retention policy; cloud audit trail sits on the vendor's infrastructure under their retention policy. Third, feedback privacy: on-prem human overrides train only your model; cloud overrides may contribute to a shared training set. The regulation does not specify on-prem — but the technical requirements it mandates (real-time oversight, data sovereignty, audit control) are architecturally easier to satisfy on-prem.
Which regulations specifically require human-in-the-loop?
The EU AI Act (Article 14) requires human oversight for high-risk AI systems — binding August 2, 2026. GDPR Article 22 gives individuals the right to human intervention in automated decisions. The NIST AI Risk Management Framework recommends human override and continuous monitoring. ISO/IEC 42001 requires continuous improvement mechanisms including human feedback loops. FDA 21 CFR Part 11 requires electronic signatures and audit trails for regulated decisions. OSHA frameworks require human oversight of safety-critical automated systems. Together, these create a converging global standard that makes HITL governance a baseline, not an option.
How does the override mechanism work technically?
The RTX AI Brain presents each recommendation on the operator's HMI dashboard with three actions: Accept (recommendation executes), Override (operator enters alternative decision + reason code), and Defer (recommendation postponed with documented justification + rescheduled date). Each action captures: timestamp, operator ID via badge/login, reason code (from a configurable dropdown), free-text justification if required, and the AI's original recommendation + confidence score for comparison. The complete decision record — AI input + AI reasoning + human action + outcome — is stored on-prem with cryptographic timestamping. Configurable per risk level: low-risk decisions auto-accept; high-risk decisions require explicit human action before execution.
How fast can we deploy HITL-compliant on-prem AI?
Eight to twelve weeks. Weeks 1-2 — governance audit: which AI decisions in your deployment are high-risk under applicable regulations, what HITL requirements apply, what override workflows are needed. Weeks 3-4 — Jetson edge + RTX deployment, AI models loaded, baseline operational. Weeks 5-6 — HITL dashboard configured: risk classification per decision type, override workflows tested, audit trail format validated against regulatory requirements. Weeks 7-8 — operator training, compliance documentation generated, governance framework validated with your legal/compliance team. The August 2026 EU AI Act deadline is 10 weeks away — an 8-week deployment fits within the window.
HITL Governance · 5 Layers · August 2026 Deadline
The Regulation Says "Human Oversight." The Architecture That Proves It Is On-Premise.
Book a 30-minute call with our governance deployment engineers. Walk through your AI risk classification, your regulatory exposure, and your HITL requirements. See the five governance layers running — input transparency, reasoning visibility, real-time override, audit trail, and feedback loop — all on-prem. Perpetual license, source code included, $0/mo.